Halaman ini belum tersedia dalam bahasa Anda. Anda membaca teks bahasa Inggris.
Solutions
Ad accounts
- 40 a day
- Page ceiling at full pace, reached on day seven
- 4 consoles
- Google Ads, Meta Ads, TikTok Ads and Microsoft Ads
- 56 rules
- 31 general tracker rules plus 25 written for the consoles
- 1 a day
- Payment edits the scenario treats as a safe day
When one ban takes five
Losing one ad account is a cost of doing business. Losing five because one was reviewed is a different problem, and it is rarely about the ban itself.
It is about what the platform can see those five accounts have in common. Open two consoles in one browser and the list is long.
One jar and one storage
The login cookie is the shortest link there is, and local storage, databases and service workers persist per browser too.
One device
Screen, cores, memory, graphics strings, fonts, timezone and language are identical in every window.
One exit address
Two consoles reached from one address minutes apart are related without anyone looking hard.
One payment identity
A saved card, an autofilled billing address and the browser's payment profile follow the browser.
How buyers handle it today
Each of the usual answers cuts one of those links and leaves the rest. A reviewer looking at one account has the others one query away.
The answer that cuts every link costs a whole machine, and its updates, for every account you run.
| Approach | Closes | Leaves open |
|---|---|---|
| An incognito window | The jar, at the end of the session | The same computer, and the session you needed to keep |
| A second browser profile | The cookie jar | One device underneath, one exit address, one saved card |
| A VPN | The address the console sees | Cookies, storage, device readings, saved billing details |
| A fingerprint extension | Some values, rewritten inside the page | Values a page can read back, and the network layer untouched |
| A machine per account | Almost everything, honestly | Gigabytes and a separate update cycle for every account |
| A profile per account | Jar, storage, device, exit address, saved billing details | Spend patterns, creatives, landing pages and complaints |
What the Ad accounts scenario sets
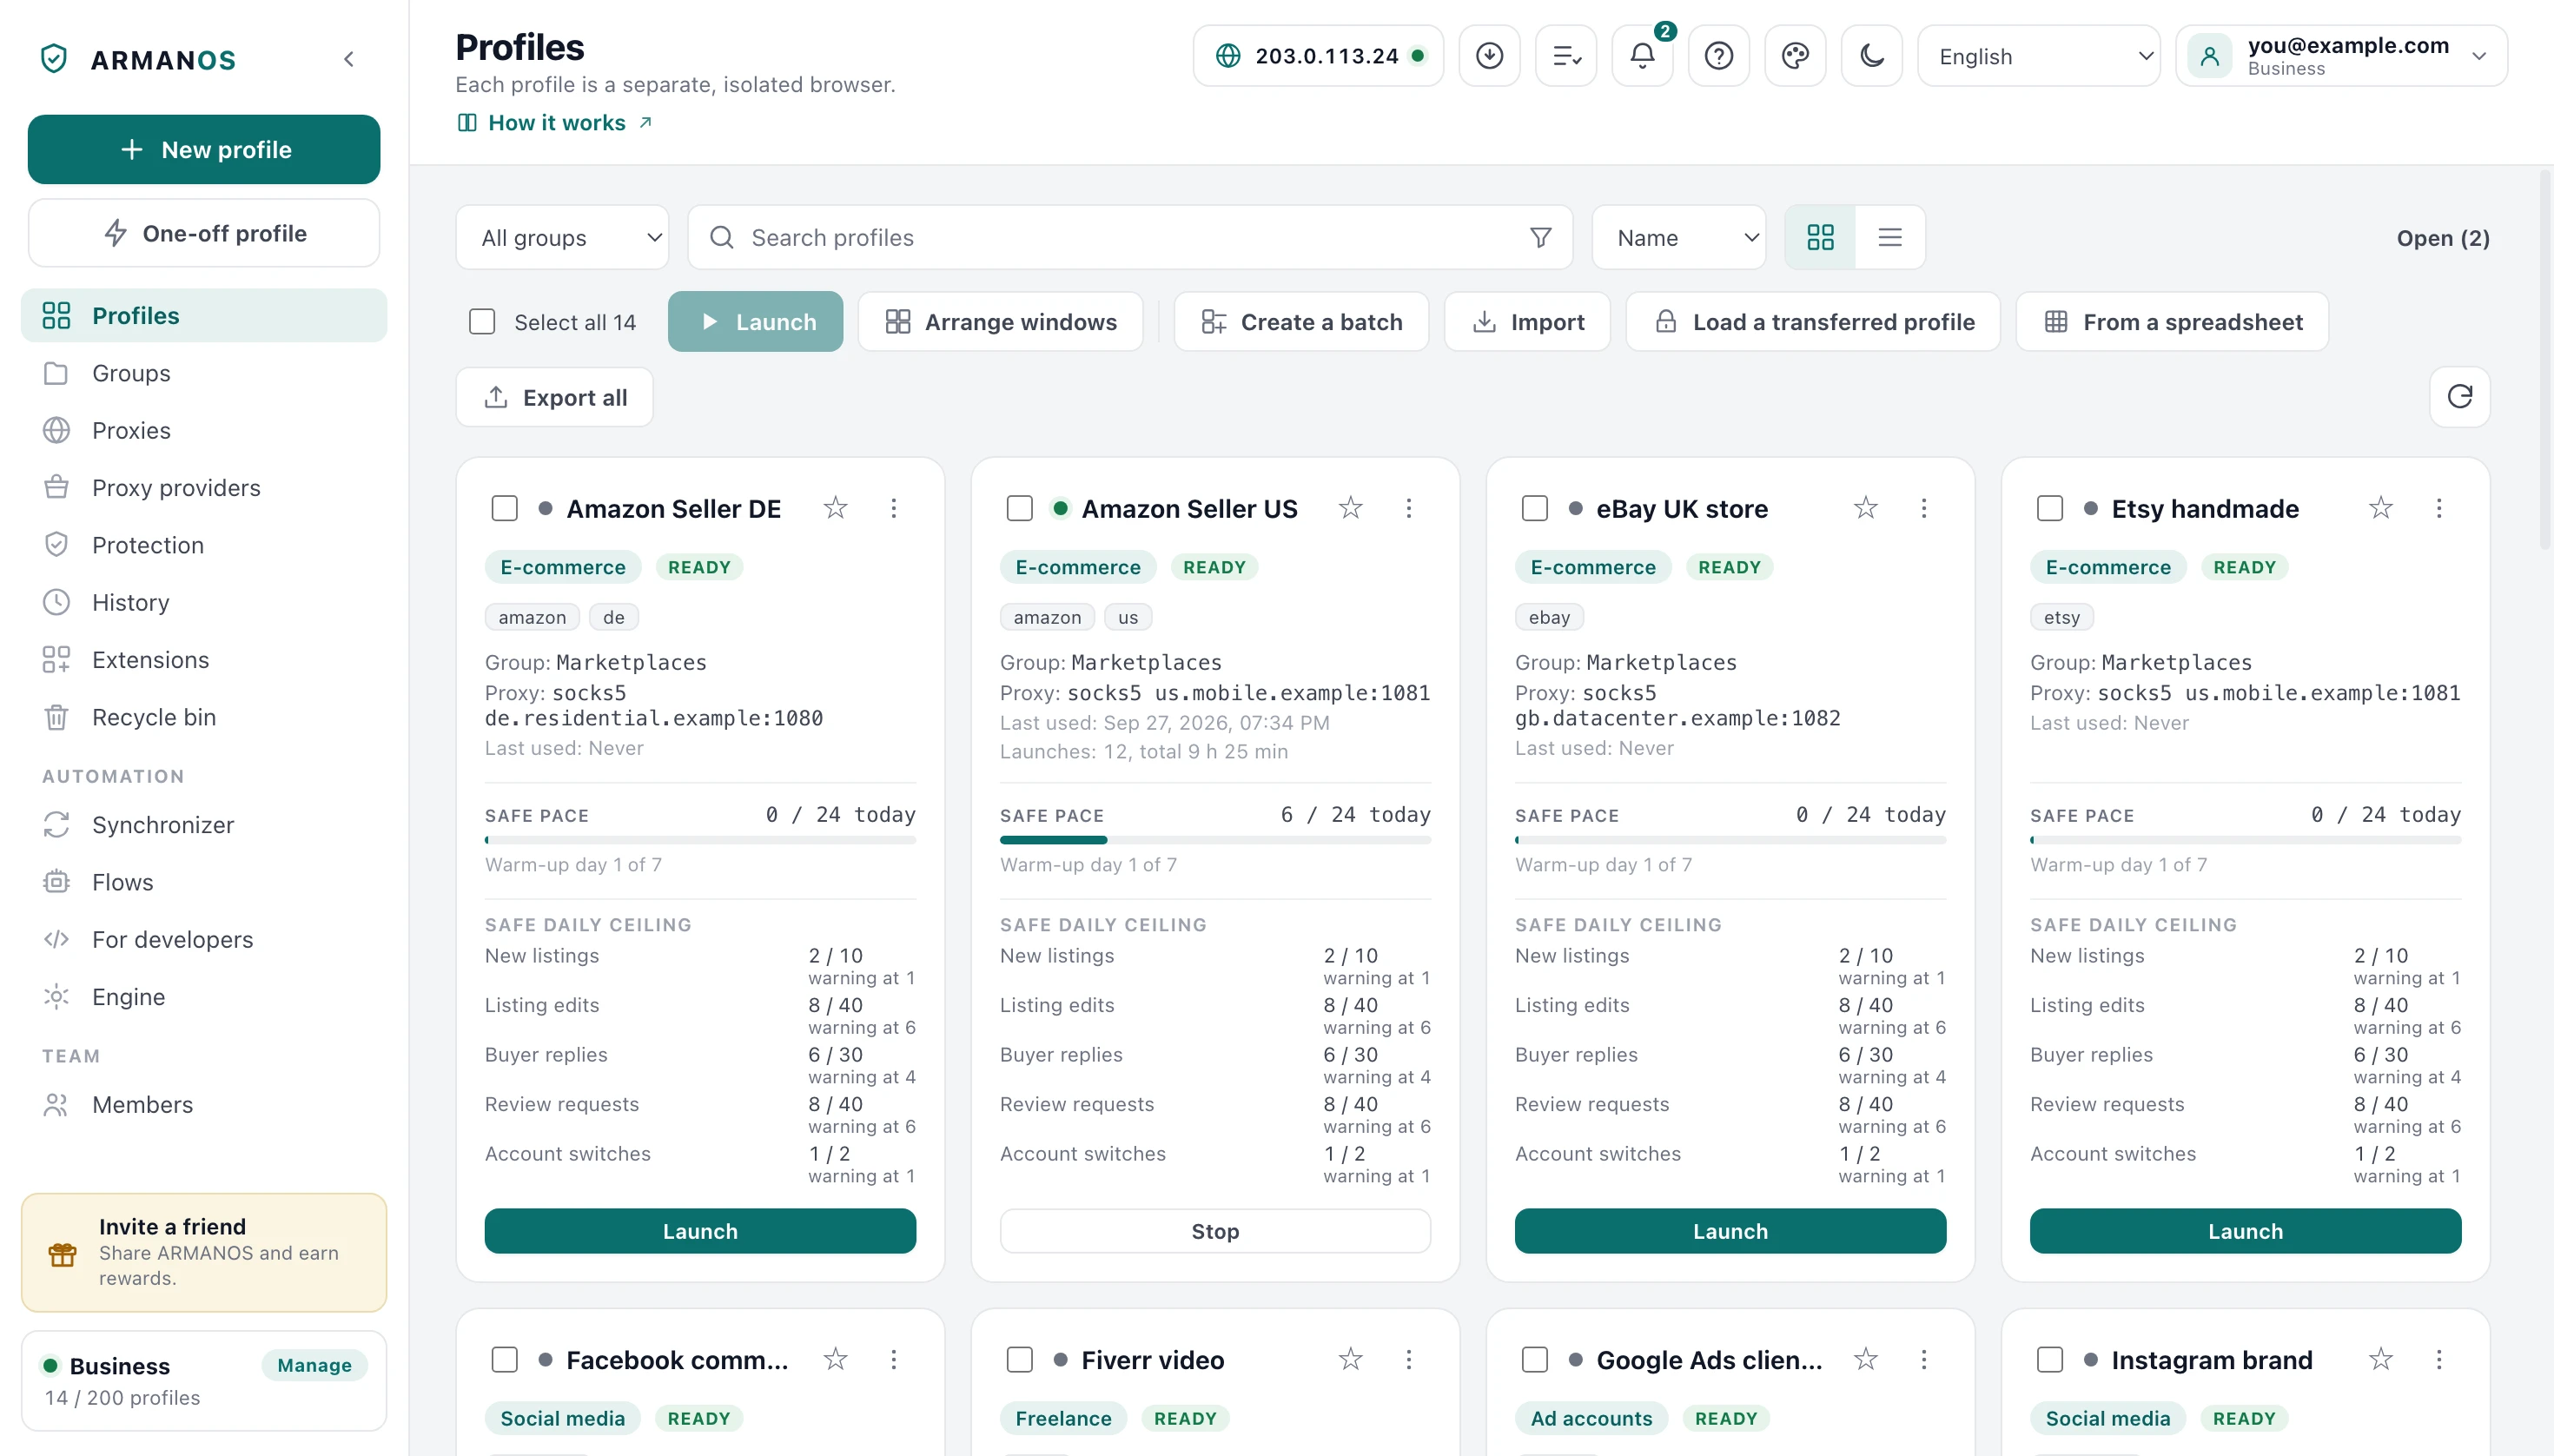
Picking a scenario sets the opening address, the tracker lists, the link cleaning, the page scripts and the rows of the Safe daily ceiling section. It is not a label on a card but a set of settings applied at every launch.
The app reads the same lines at launch and again when it draws the card.
- scenario id
- ads
- opening address
- https://ads.google.com
- tracker lists
- general + ads, 56 rules
- page scripts
- fingerprint, stealth
- link cleaning
- on, 40 parameters
- daily page ceiling
- 40, warm-up over 7 days
- safe daily ceiling
- 5: campaign edits, budget changes, new campaigns, payment edits, account switches
- consoles
- Google Ads, Meta Ads, TikTok Ads, Microsoft Ads
The record read out of the code rather than written for this website. Link cleaning covers every console's click identifier: gclid, wbraid, gbraid, msclkid, fbclid and ttclid among them.
What the ad list cuts
A blocklist built for privacy browsing is the wrong instrument inside an ad console. Cut one request too many and a creative will not upload.
What is left is cross-account correlation: conversion and audience pixels, signal endpoints, the third parties that sell the join. Requests a console needs in order to sign in, bill or work are excluded on purpose.
| Console | Rules in the ad list | What they match |
|---|---|---|
| Google Ads | 8, plus 4 first-party | Conversion and audience pixels, tag services, and the console's own gen_204, jserror and csi beacons |
| Meta Ads | 4, plus 1 first-party | The signals script, fbevents.js, the tr pixel, and the ajax/bz logging call on facebook.com |
| TikTok Ads | 2 | Both analytics hosts, including the Singapore one |
| Microsoft Ads | 4 | The Bing click and log endpoints and the MSN event host |
| Any site | 7 third-party | The identity graph: adsrvr, demdex, rlcdn, agkn, crwdcntrl, scorecardresearch, everesttech |
Blocking is not the feature here
The device the console sees
The fingerprint is derived at launch from the same inputs, so an account does not find its computer changed overnight.
Template
One of five: macOS, Windows, Linux, Android phone, Android tablet.
Profile id
Seeds the graphics pair, the screen and the platform version out of generation 4's pools.
Proxy country
Measured through the proxy itself, then mapped to a timezone and a language stack that agree with it.
Engine version
The user agent and the client hints carry the version of the engine that renders the page.
The buyer's own machine stays out
That is what makes a shared profile usable in an agency. A media buyer opening it on their own laptop gets the readings the account saw yesterday, and their real machine does not leak into it.
WebRTC is not offered a way around the proxy
Card and login stay local
A saved card, a billing address and an autofilled name are browser data, and every profile has a directory of its own. Two ad accounts are two directories.
The account password does not reach our server
The account's own login pair is held by the app (Sign-in details in the profile menu) rather than by the browser, and never sent to our server. A synced profile carries its id, name, group, scenario, template, proxy and tags, and no field for the login password.
The profile directory
Cookies, storage, service workers, saved cards and autofill.
The account password
Written beside the profile. The system seals it on Windows only: on macOS the key ships inside the program, and on Linux it is written as typed.
The one-time code
The secret belongs to the profile, and the code is generated beside it.
The proxy password
Never placed on the command line, where a credential shows up in any process listing on the machine.
The browser's own keys
The engine encrypts its own cookie and password store instead of asking the system for a key, which keeps a live session portable.
One group per media buyer
A role covers the whole workspace, so a role alone cannot hide clients from a new buyer. Group access narrows it, one row per member per group.
Once access is set, a member never sees a profile that is in no group, and opening one by its id gives them profile not found rather than forbidden.
Owner
Everything, and cannot be removed from their own workspace or restricted to groups.
Admin
Billing, the team, the history, other members' profiles and machines. Hands out group access.
Manager
Shared working resources: groups and the proxy library, including Change IP on a mobile proxy. No money, no team.
Operator and member
Work with the profiles they were given, inside the groups they can see. Change nothing shared.
No groups chosen
The member sees every group, and the window says so. Taking their last group away does not strip their access, it opens everything.
Seats
Business includes 3, Enterprise 20, and additional seats are 3 dollars a month each.

While signed in the second machine sees who opened the account
What the ceilings count
The page counter is the only number the app measures. It counts top-level navigations, survives a relaunch on the same day and starts fresh at midnight.
The five rows of the Safe daily ceiling section are numbers, not counters, ramped by the same curve. Payment edits are the strictest, because that change is the likeliest to put a human reviewer in front of the account.
| What the scenario counts as a day | Full ceiling | Day one of the ramp | Warning at |
|---|---|---|---|
| Campaign edits | 12 | 2 | 70 percent |
| Budget changes | 4 | 1 | 50 percent |
| New campaigns | 3 | 1 | 67 percent |
| Payment edits | 1 | 1 | 99 percent |
| Account switches | 3 | 1 | 67 percent |
| Pages opened (measured) | 40 | 8 | 80 percent |
What this does not do
- It does not prevent bans. Spend patterns, creatives, landing pages, complaints and account age are all reviewed, and none of them is a browser question.
- It does not hide your address by itself. Without a proxy the profile goes out from your own address, and the app says so in its first-steps list.
- It does not count what you do inside a console. Only pages opened in the profile are measured; the five rows of the Safe daily ceiling section are guidance you follow yourself, and nothing is blocked.
- It does not create or warm up ad accounts. The warm-up ramp is a number on a bar, not activity on your behalf.
- It does not know how old an ad account is. The day counter is the age of the ARMANOS profile, which is all the app can honestly see.
- The engine work is not finished. A few readings are still corrected from the page rather than inside the engine, and the remaining list is closed build by build.
How to check
Every claim above is one file away. These are the lines that hold it and the stands that break if it stops being true.
- The Ad accounts scenario is one record, and the app shows exactly its numbers
- packages/shared/src/index.js (SCENARIOS.ads) · apps/desktop/src/main/main.js (actionLimitsFor, paceInfoFor)
- A rule fires only when the address carries the console host
- apps/desktop/src/lib/tracker-rules.js (TELEMETRY_BY_SCENARIO)
- Each profile is its own directory, and the proxy password never reaches the command line
- apps/desktop/src/lib/forkEngine.js (profileDir, proxyArg) · apps/desktop/test/proxy-auth-bridge.js
- The account password and the one-time code secret stay on your machine
- apps/desktop/src/lib/profiles.js · apps/desktop/test/login-in-keychain.js
- Group access hides a profile even from a member who knows its id
- apps/server/src/profiles/profiles.service.ts · apps/server/test/group-access.js
- Two machines cannot hold the same ad profile at the same time
- apps/server/src/profiles/profiles.service.ts (LOCK_TTL_MS) · apps/server/test/profile-lock.js
Questions
- What happens to the other accounts when one goes?
- They keep working through the ban and the appeal. The lost account's cookies and storage sit in one directory and touch nothing else.
- Can I duplicate a profile for a replacement account?
- Yes. The copy (Duplicate in the profile menu) carries the scenario, the group, the tags, the opening address, the extensions, the proxy and the measured exit country, and it deliberately leaves out the login pair and the one-time code secret.
- Why does a copy get a different device?
- Because the fingerprint is derived from the profile id, and a copy is a new profile with a new id. Two profiles wearing one fingerprint would be tied together more tightly than anything else here could tie them.
- Should the replacement reuse the old proxy?
- Only if you mean to make that link. Pointing a new account at the exit address the lost one used is a decision, not a leftover.
- What does Delete permanently erase?
- The running browser is closed first, then the directory is erased, then the profile is cleared out of the launch notifications, the blocked-request counters and the Safe pace counter.
Next to this
Proxies
The proxy library, the measured exit country and the loopback bridge that carries the password.
Team
Seats, the five roles and group access, screen by screen.
Safe pace and warm-up
Where the numbers come from, and what the app counts against them.
Agencies
Running many clients out of one workspace.
ARMANOS Browser
The Chromium build that carries the substitution in C++.
Fingerprint tool
12 values, taken from your own browser right now.
Start with one client and two profiles
The Free plan gives you two profiles for good, with no card. macOS 13 and newer on Apple Silicon or Intel, Windows 10 and 11 on 64-bit, Ubuntu 22.04 and newer on 64-bit.